Incident Response Readiness for enterprise
See how ready your team is to respond to an incident in minutes, across every tool and format you use to document procedures. Test your readiness, adapt to change, and close the gaps you find every day.
Incident Response Readiness is fragmented
Critical knowledge, processes, and evidence are scattered across teams and tools, making readiness difficult to maintain as environments evolve.

No one has the whole picture
Procedures live across SOAR, Confluence, shared drives, and people’s heads.
Piecing them together manually makes it hard to maintain a clear, current view as the environment changes.

Readiness decays over time
Infrastructure, tooling and teams change continuously. Procedures don't. Playbooks drift away from reality.
Governance becomes an afterthought.

Gaps surface at the worst moment
New threats and environment changes can expose missing playbooks.
Creating them from scratch under pressure takes time, leaving critical gaps open when they matter most.
A continuous approach to
Incident Response Readiness
Not a wiki. Not a SOAR. Not a compliance tool you open twice a year. Cymph is the operational backbone your team already needs. It's where readiness lives, gets tested and proven.
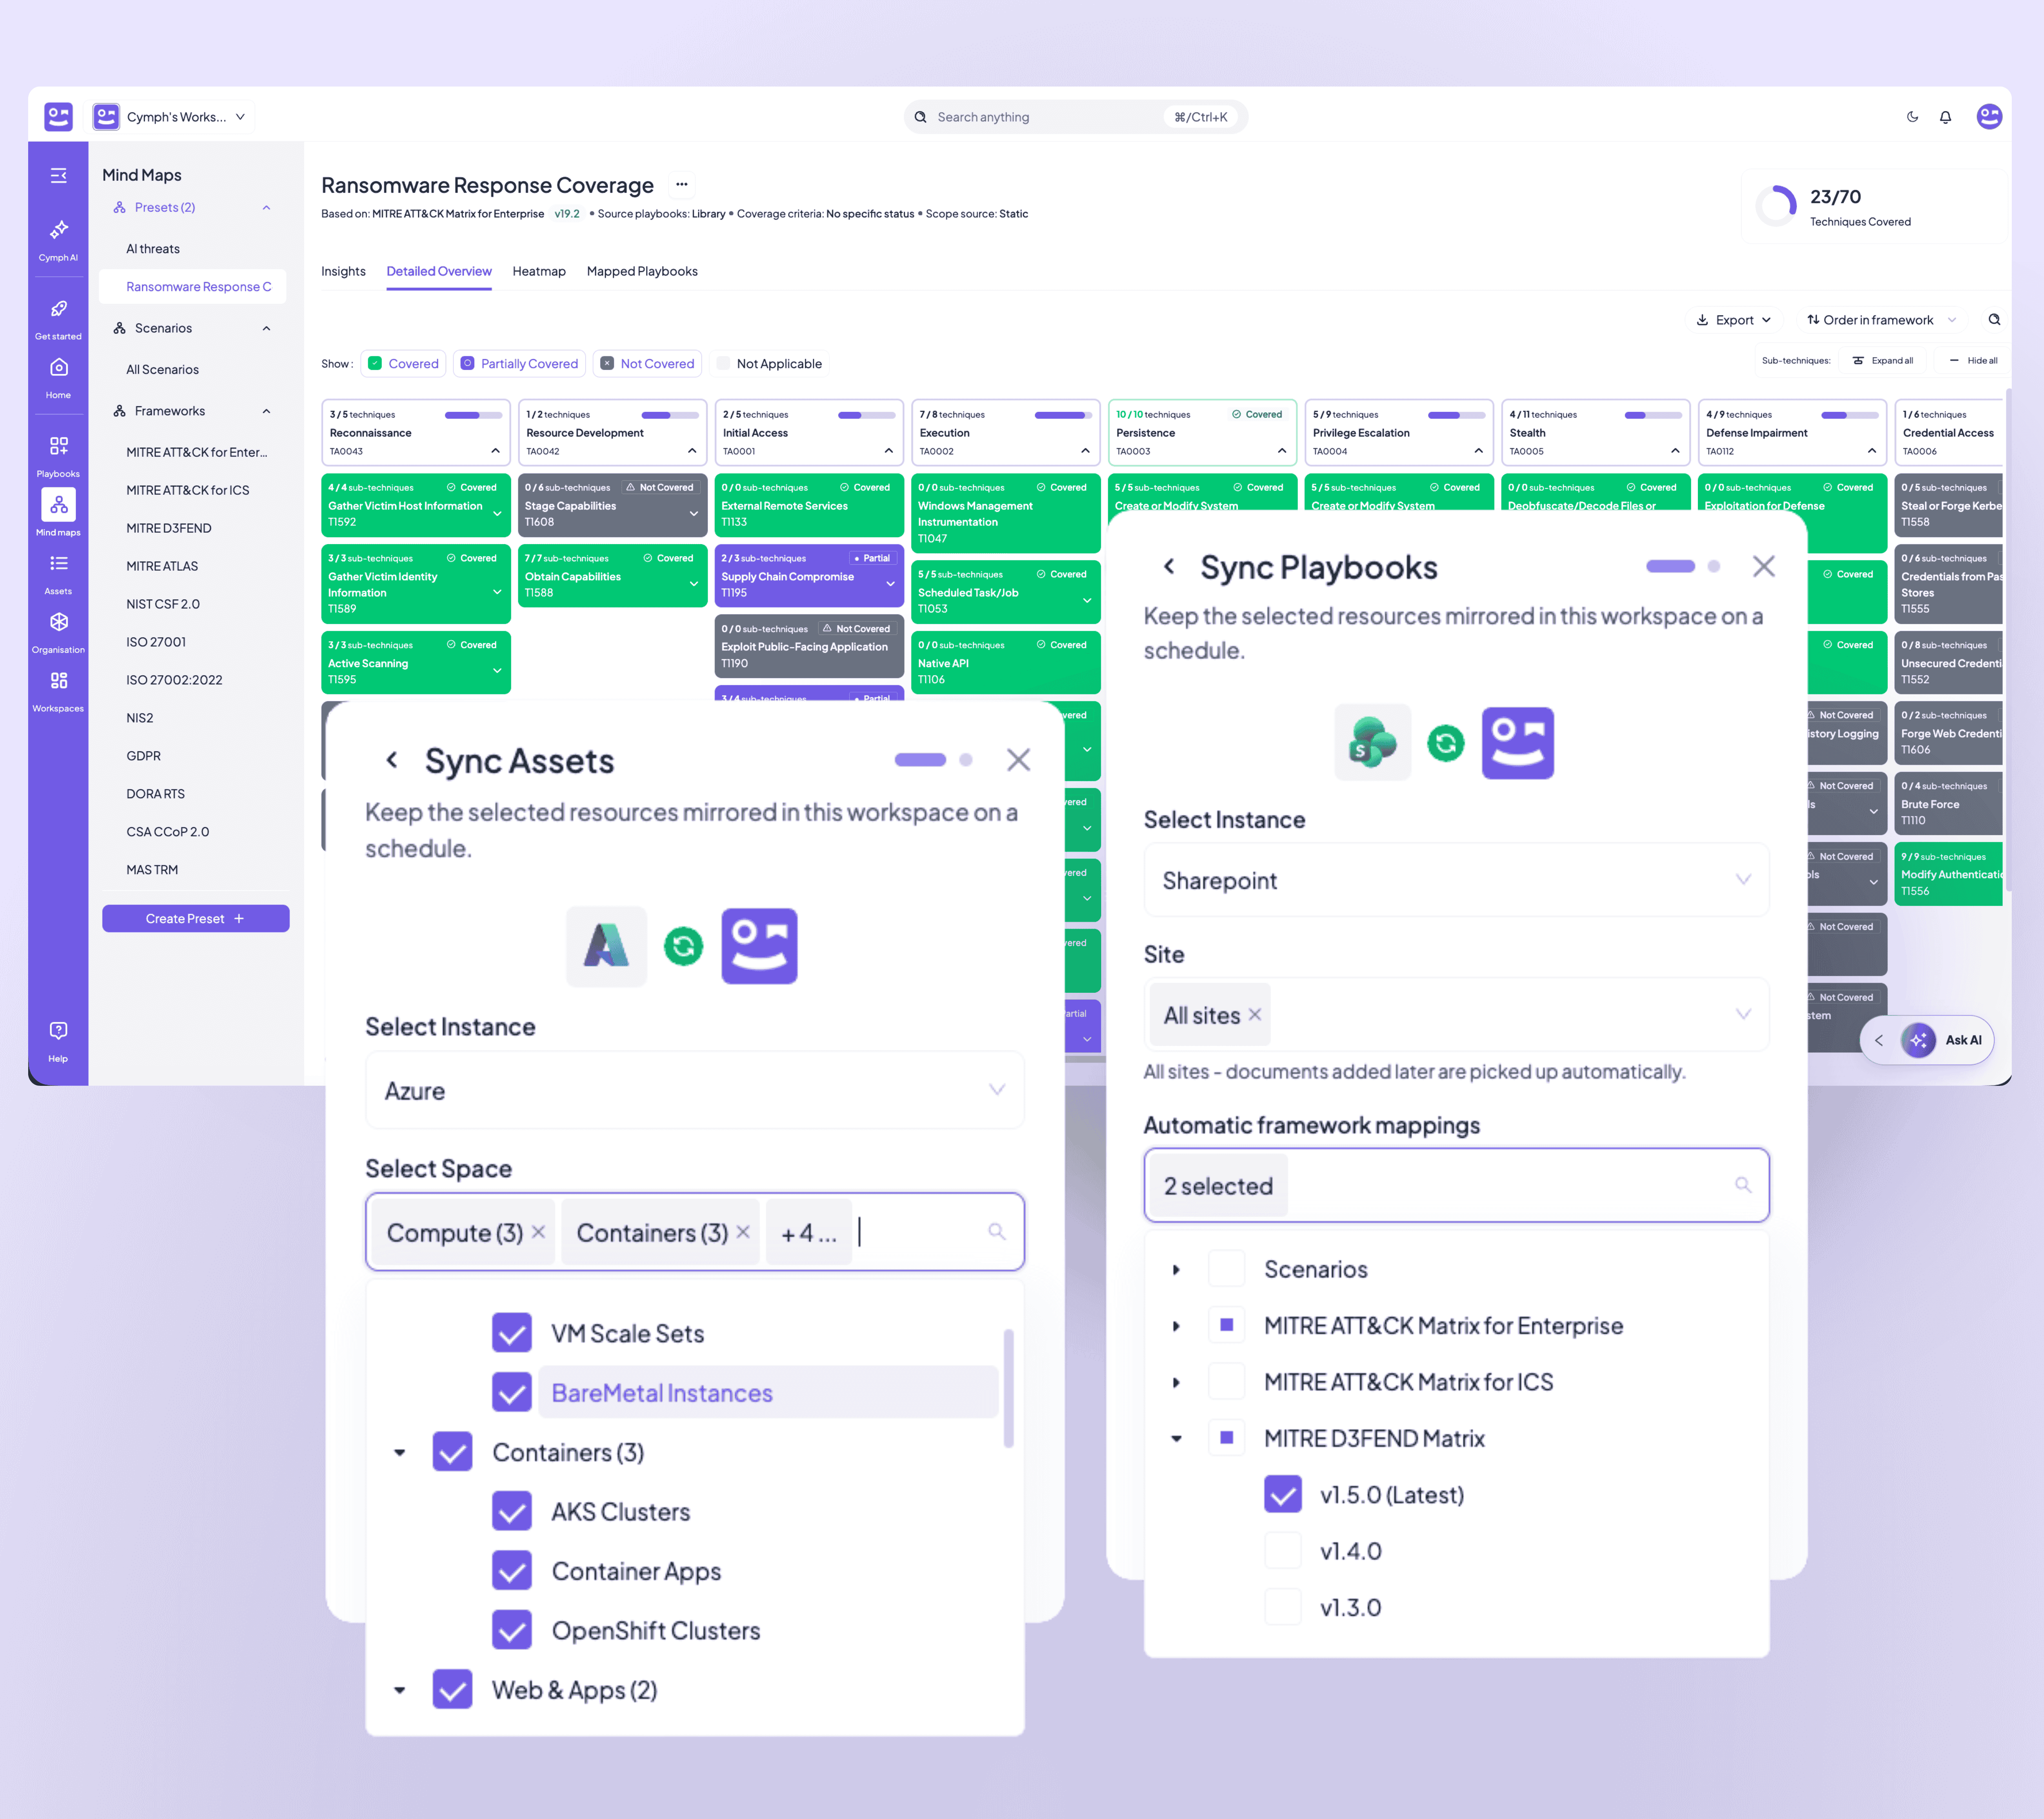
One view across your security stack
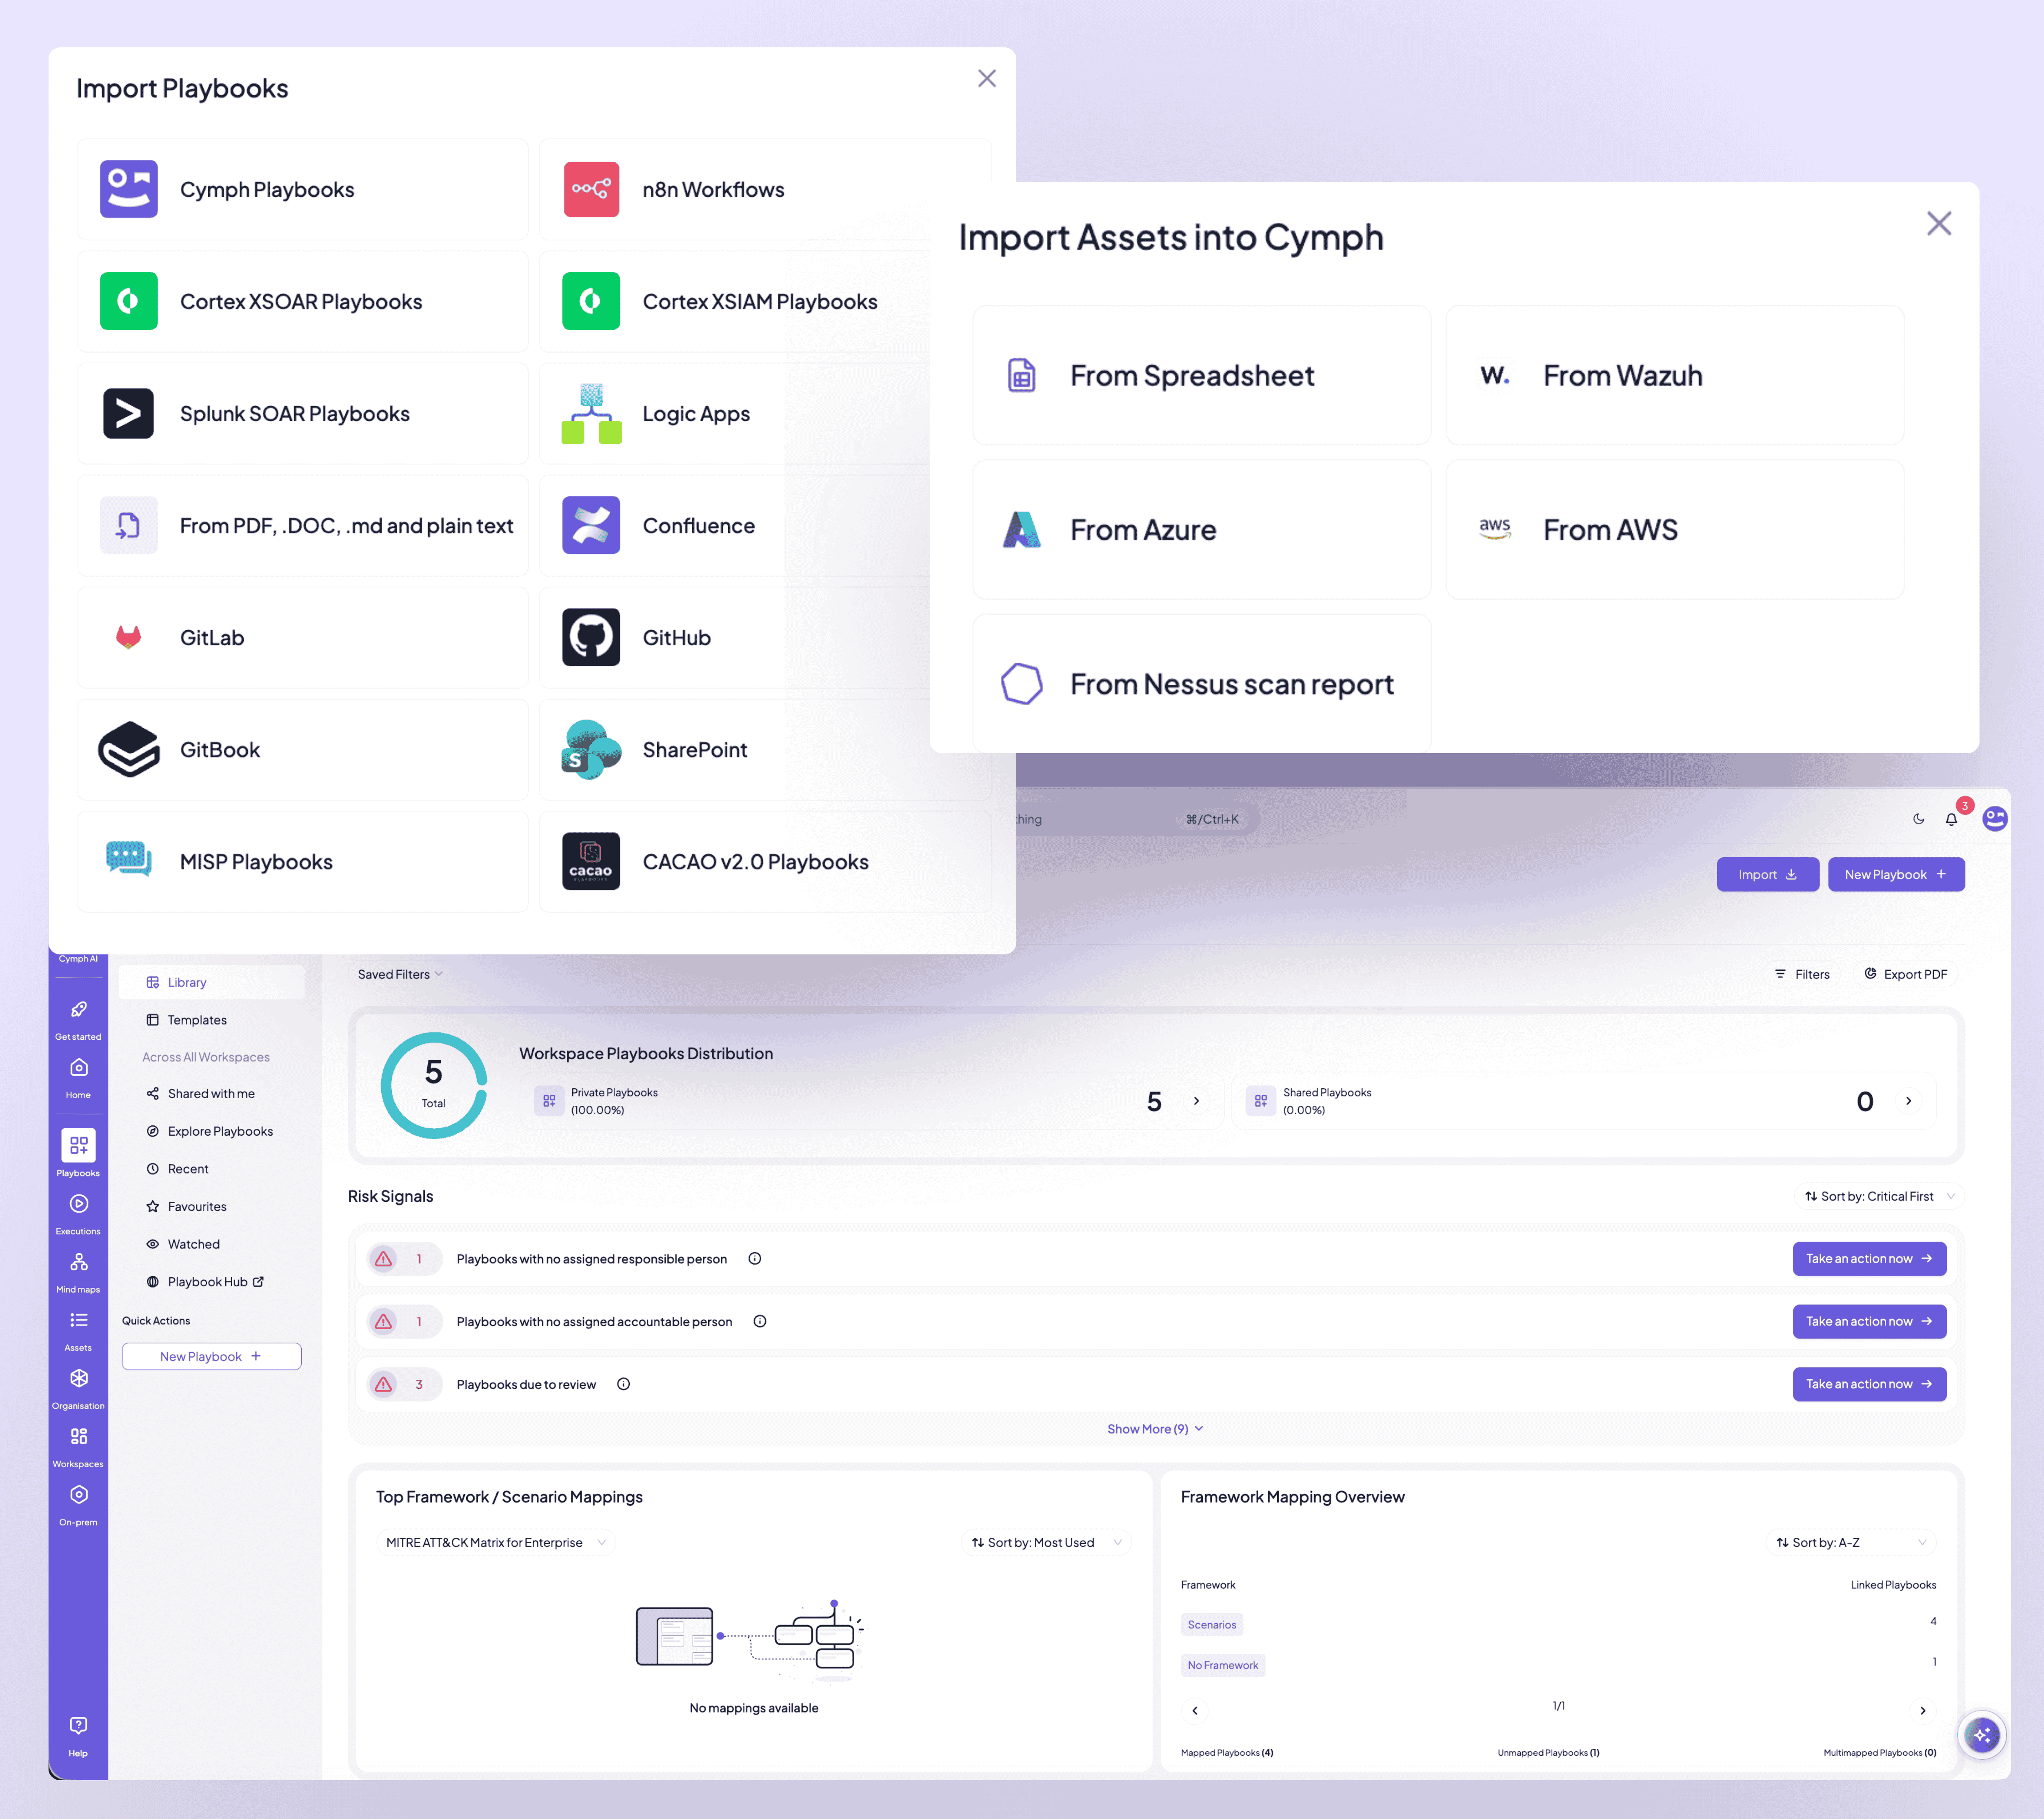
Bring fragmented response content together into one clear, unified view.
- Connect procedures from SOAR, SIEM, Confluence, SharePoint, PDFs, and other tools your team already uses.
- See your response coverage in one place, without being limited by individual vendors or disconnected systems.
- Keep a consistent view, even as your tools, infrastructure, and procedures evolve.
Always know how ready you are
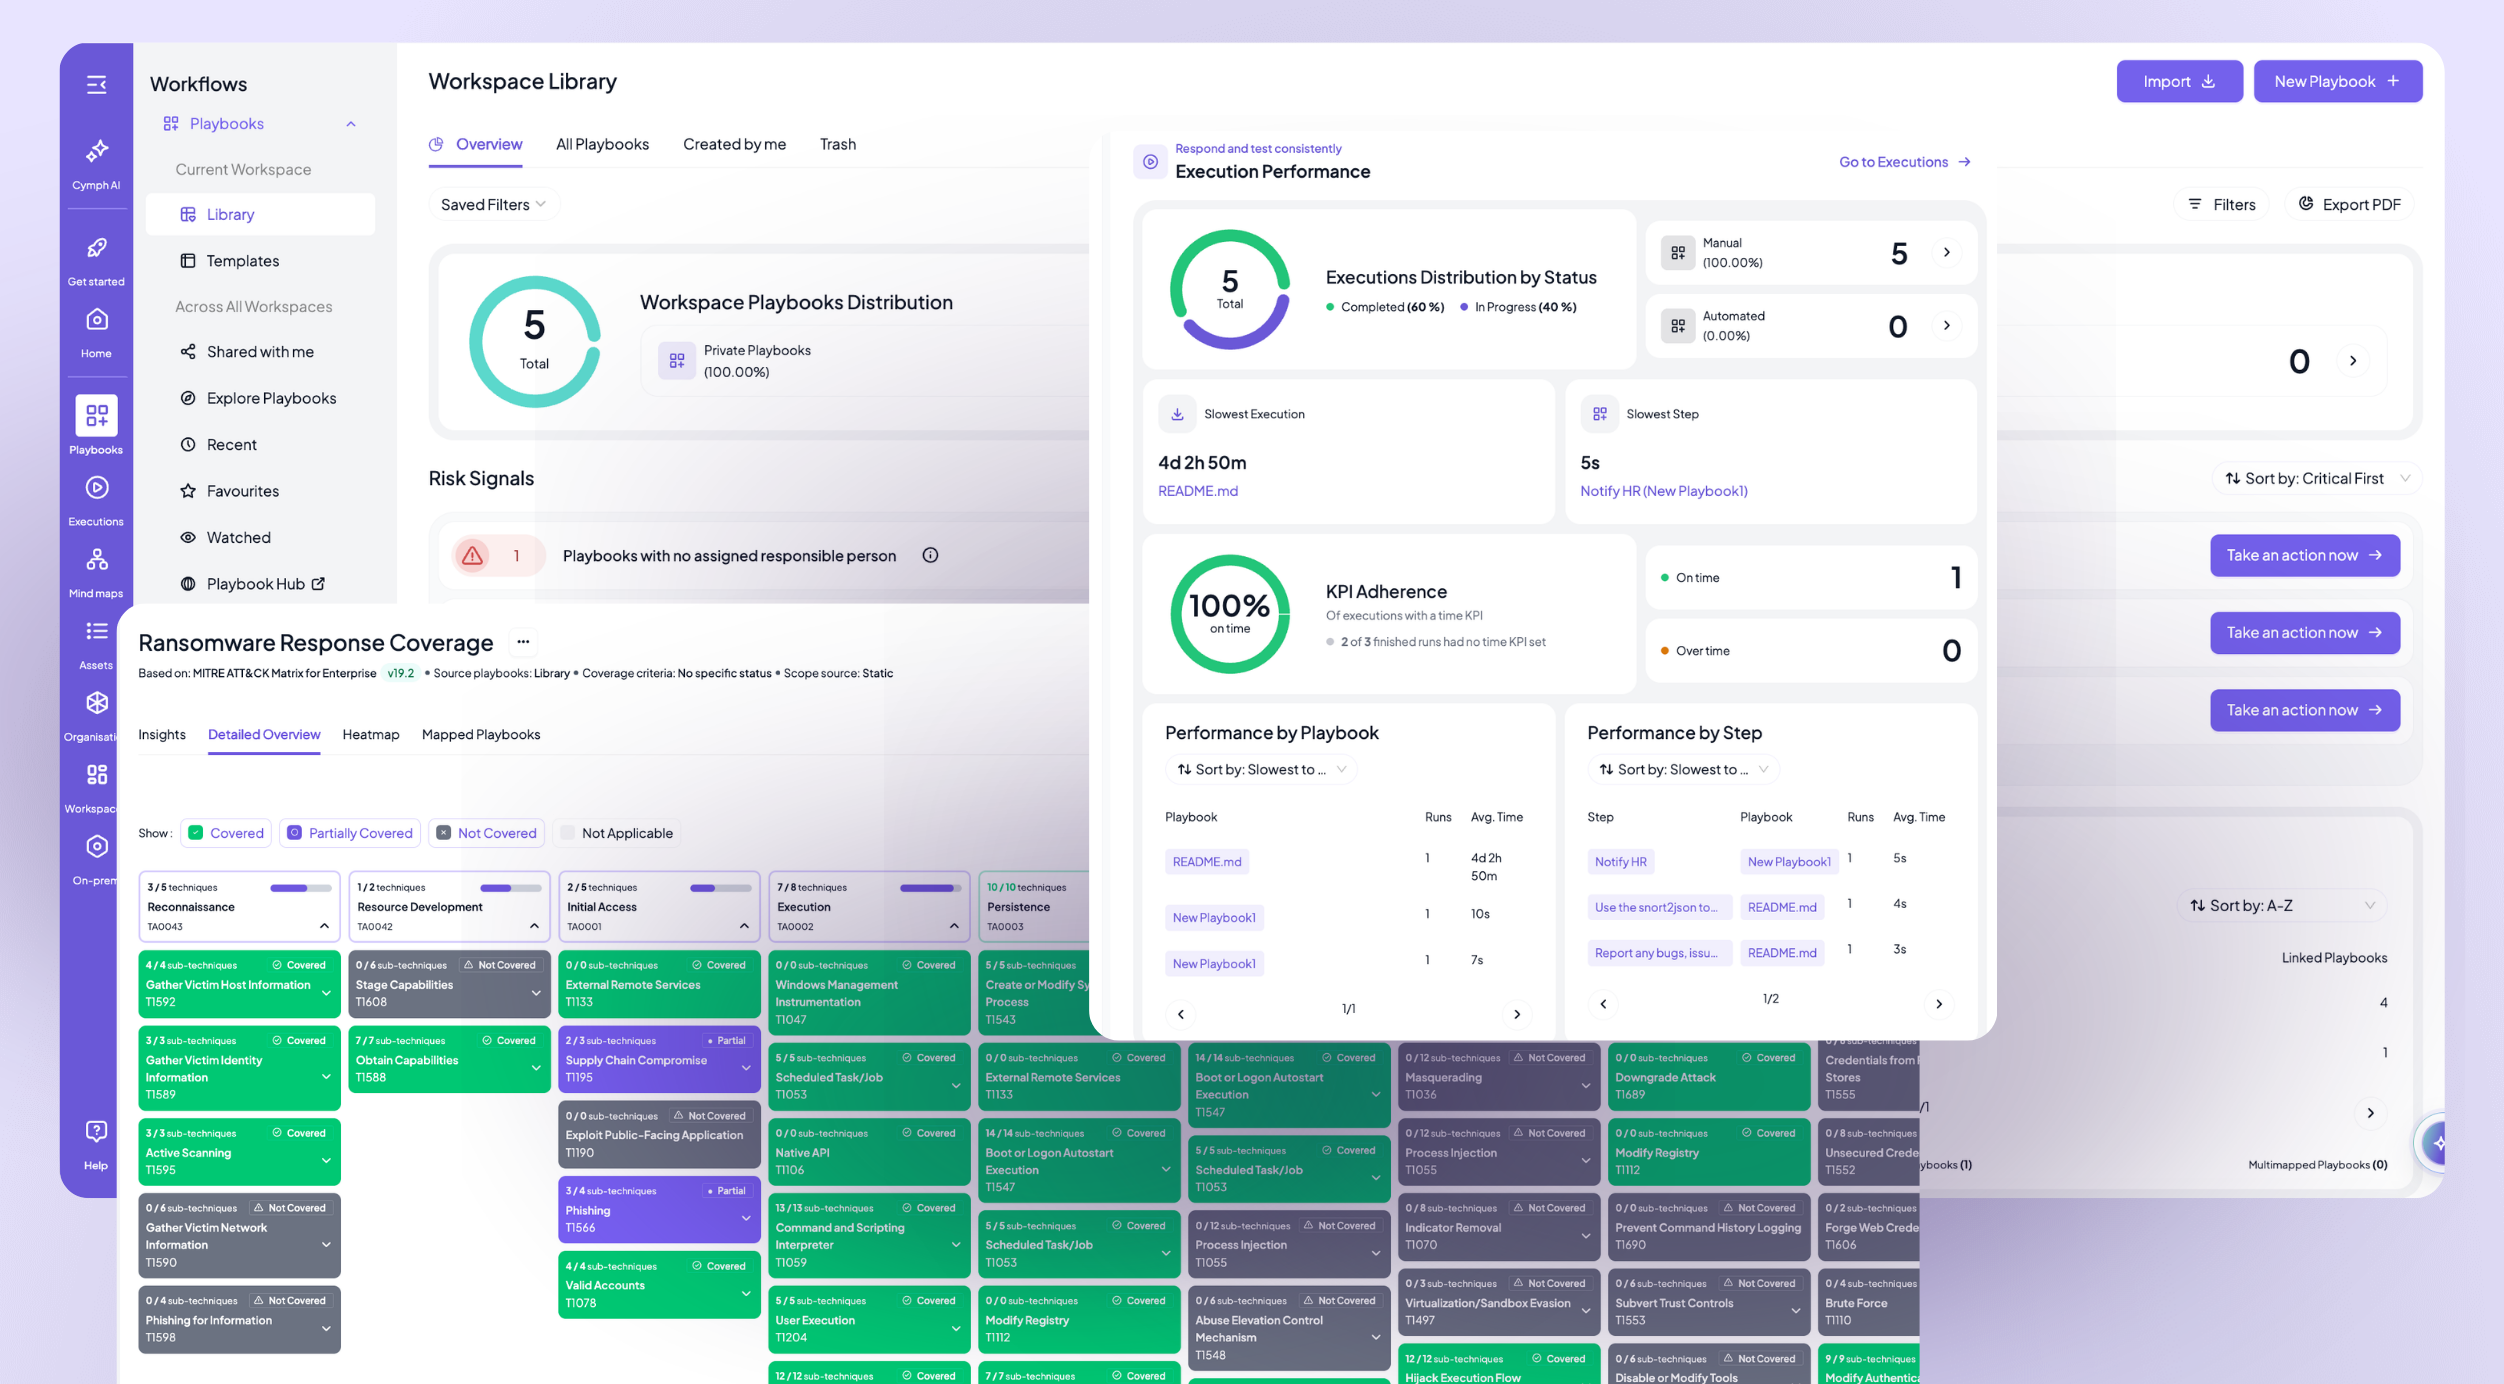
Keep a continuously updated view of your incident response readiness.
- Automatically reflect changes as procedures and playbooks are updated across your environment.
- Replace ad-hoc efforts, scripts, and point-in-time snapshots with continuously maintained response coverage.
- Stay audit-ready with clear visibility into how prepared your organisation is to respond to threats.
Find & fix the gap. Put it into action
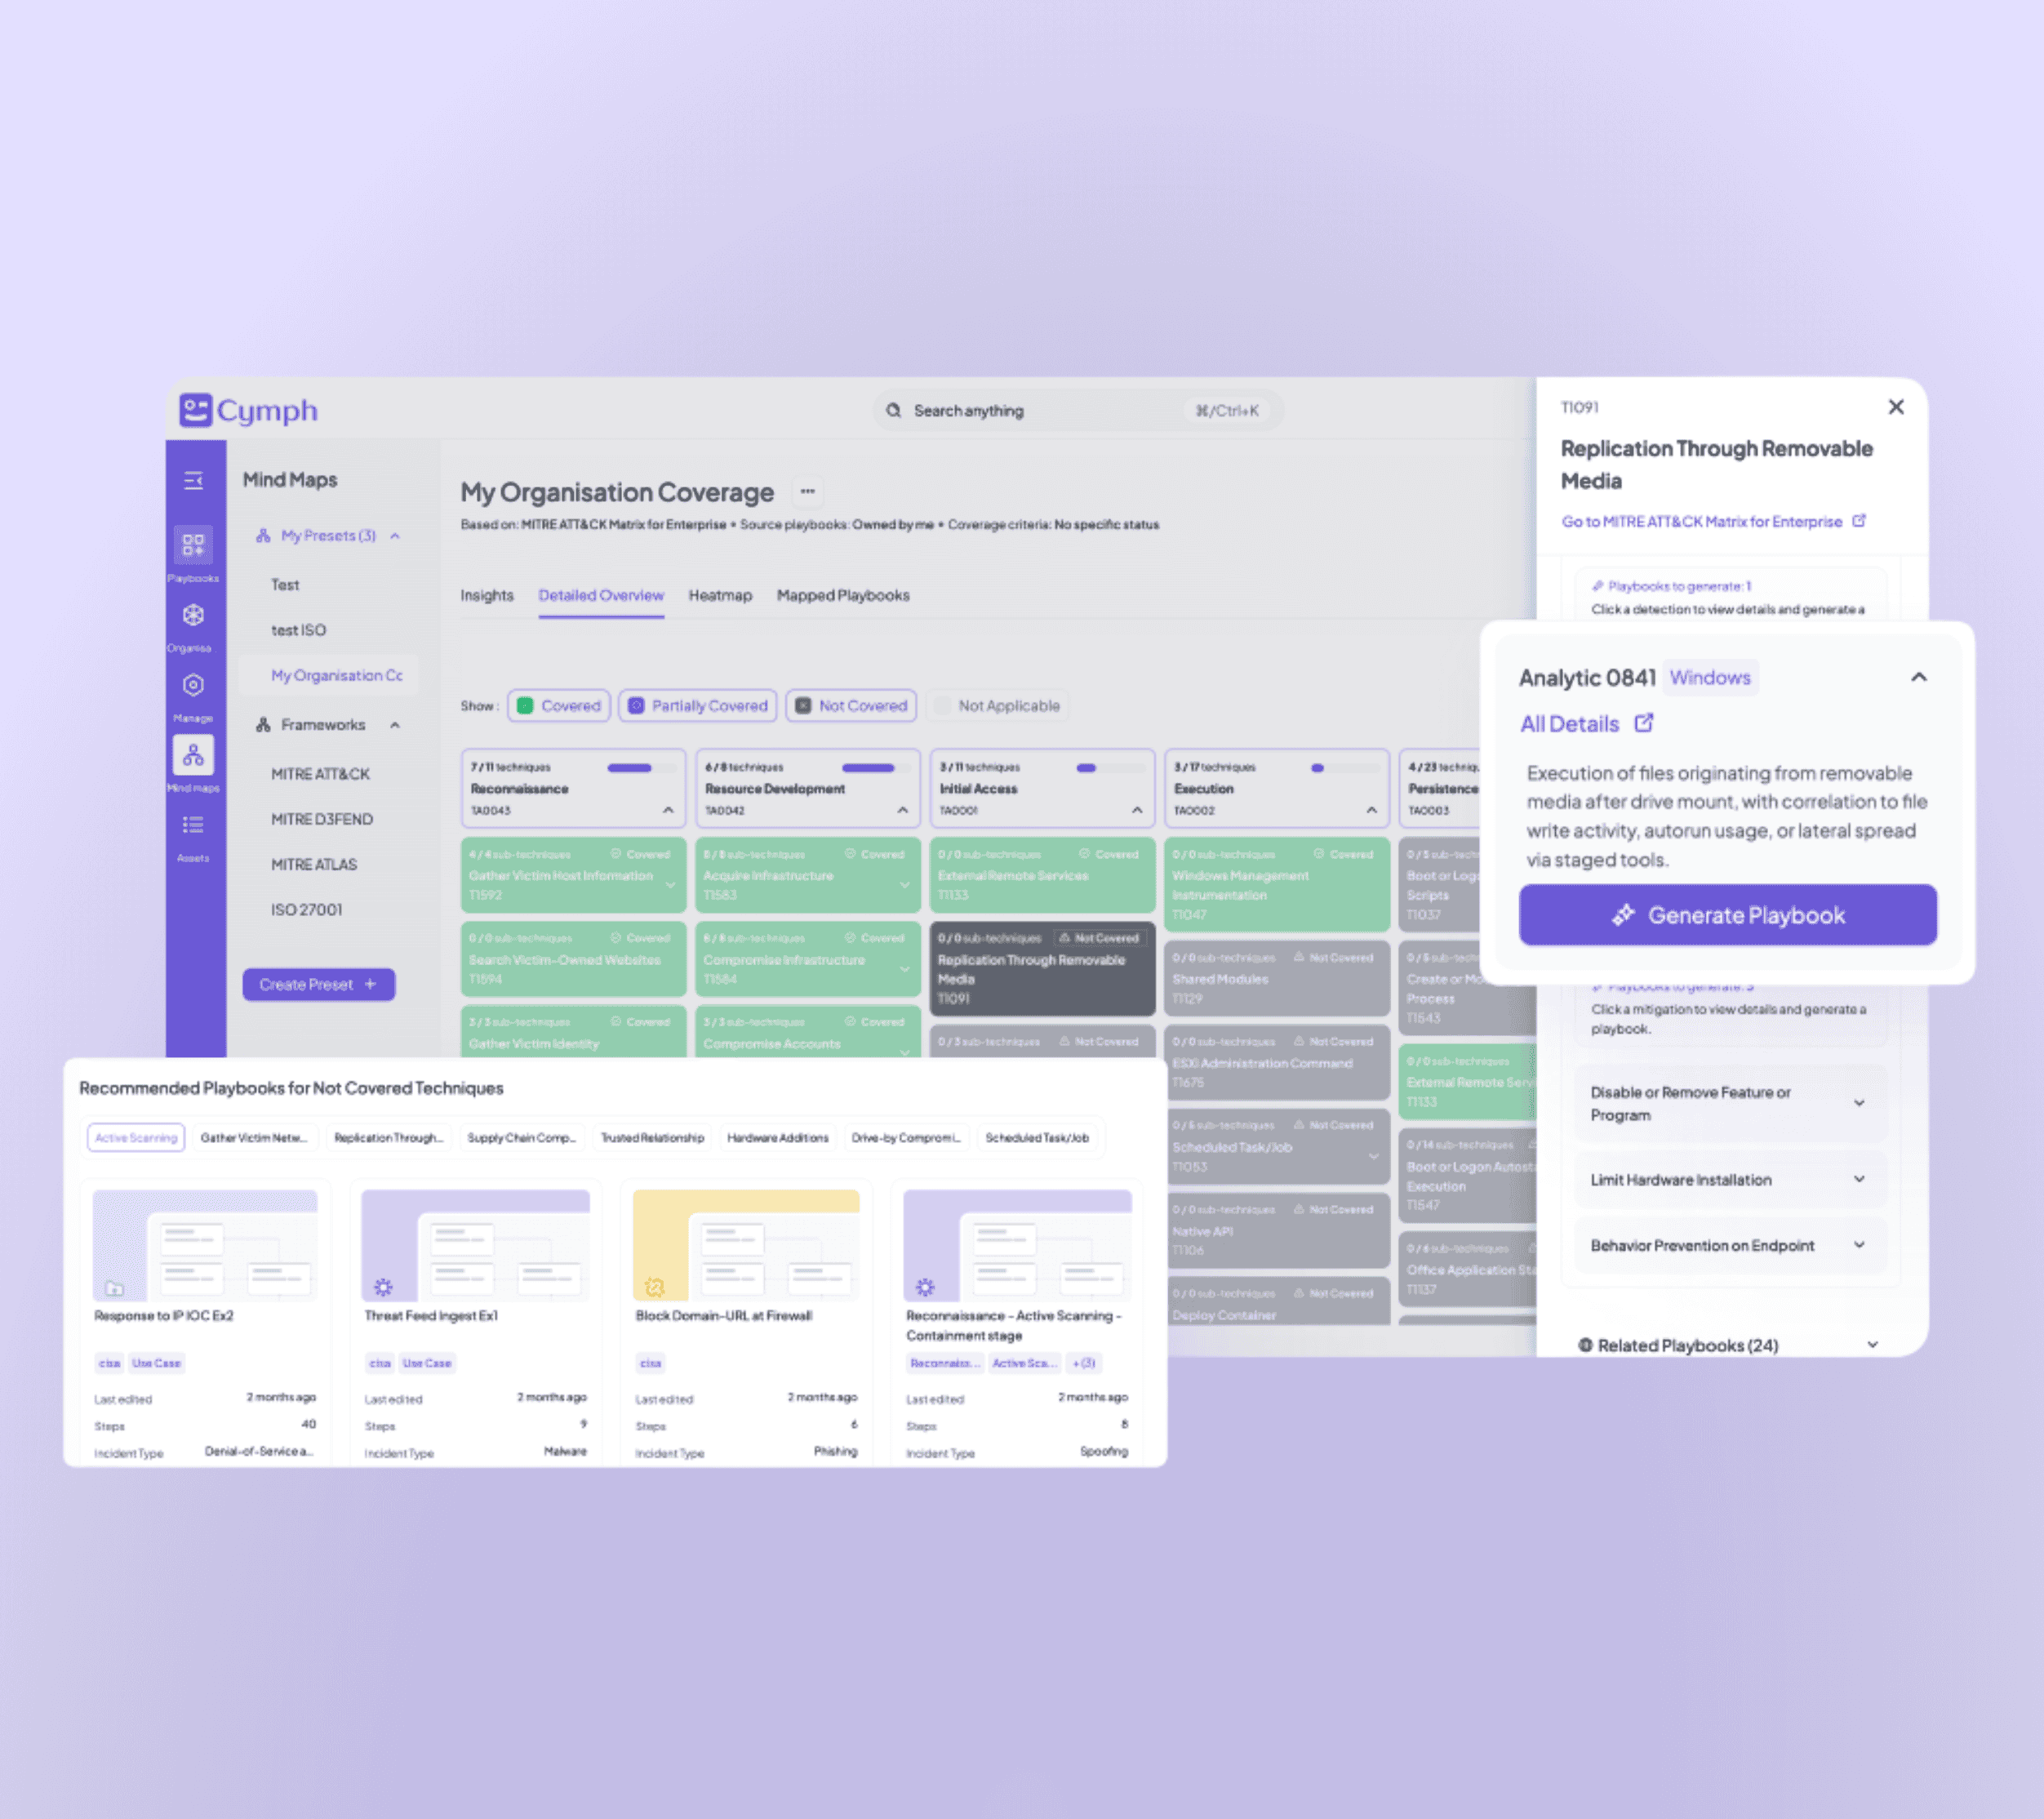
Move from identifying response gaps to fixing and deploying them in one platform.
- Identify missing ownership, outdated steps, incomplete procedures, and other gaps as your environment changes.
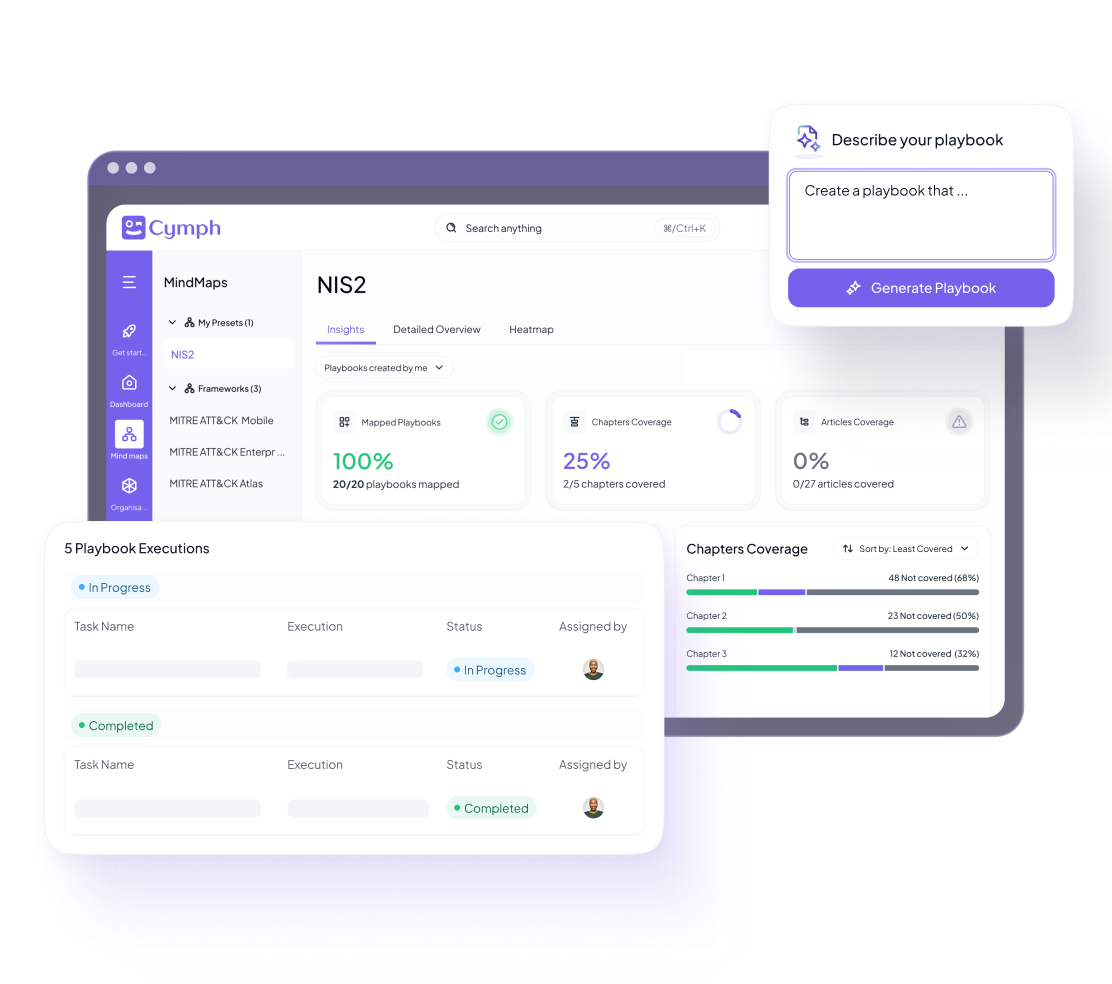
- Use AI to create a draft procedure, then refine it based on the operational context of your environment.
- Deploy improvements back to approved systems and continuously refine procedures using context, execution history, and lessons learned.
Test, respond & adapt confidently
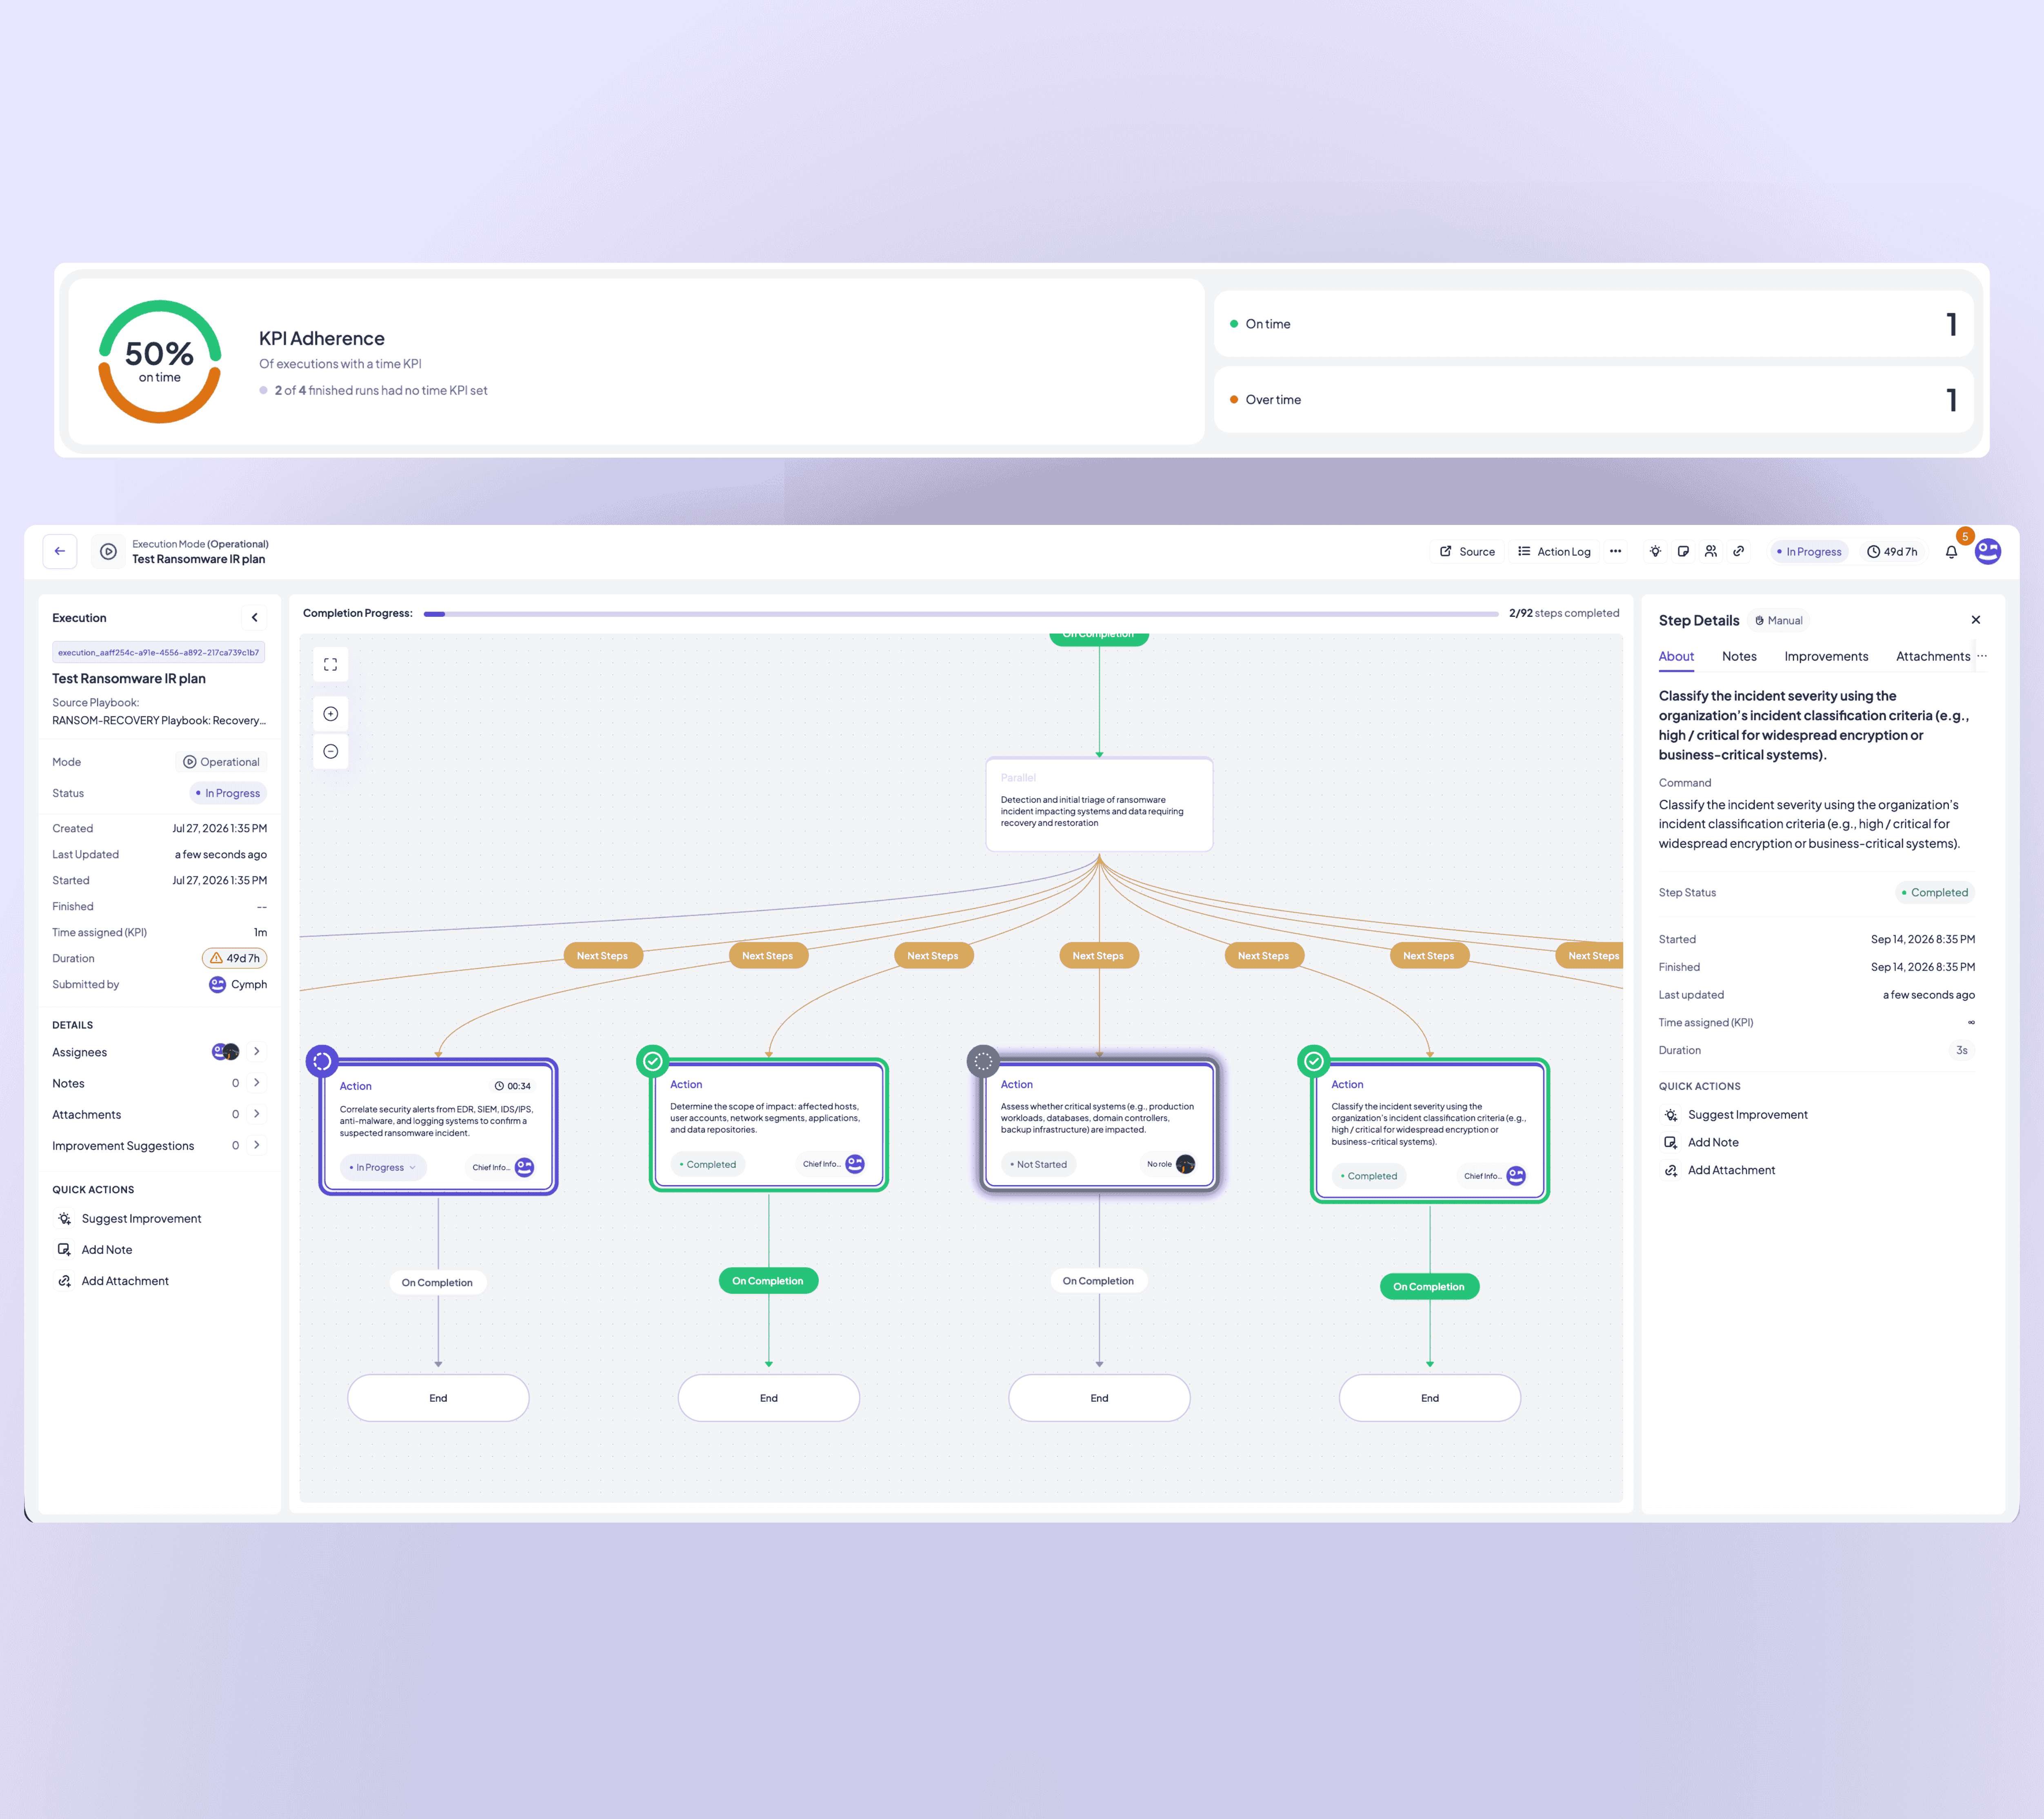
Give responders one workspace to coordinate execution when every step matters.
- Execute playbooks step-by-step while keeping stakeholders aligned around the same approved procedure.
- Assign tasks, track progress, and capture performance metrics and key decisions throughout incidents and exercises.
- Feed lessons learned and key metrics back into your procedures so future responses benefit from what your team has learned.
Readiness regenerates continuously
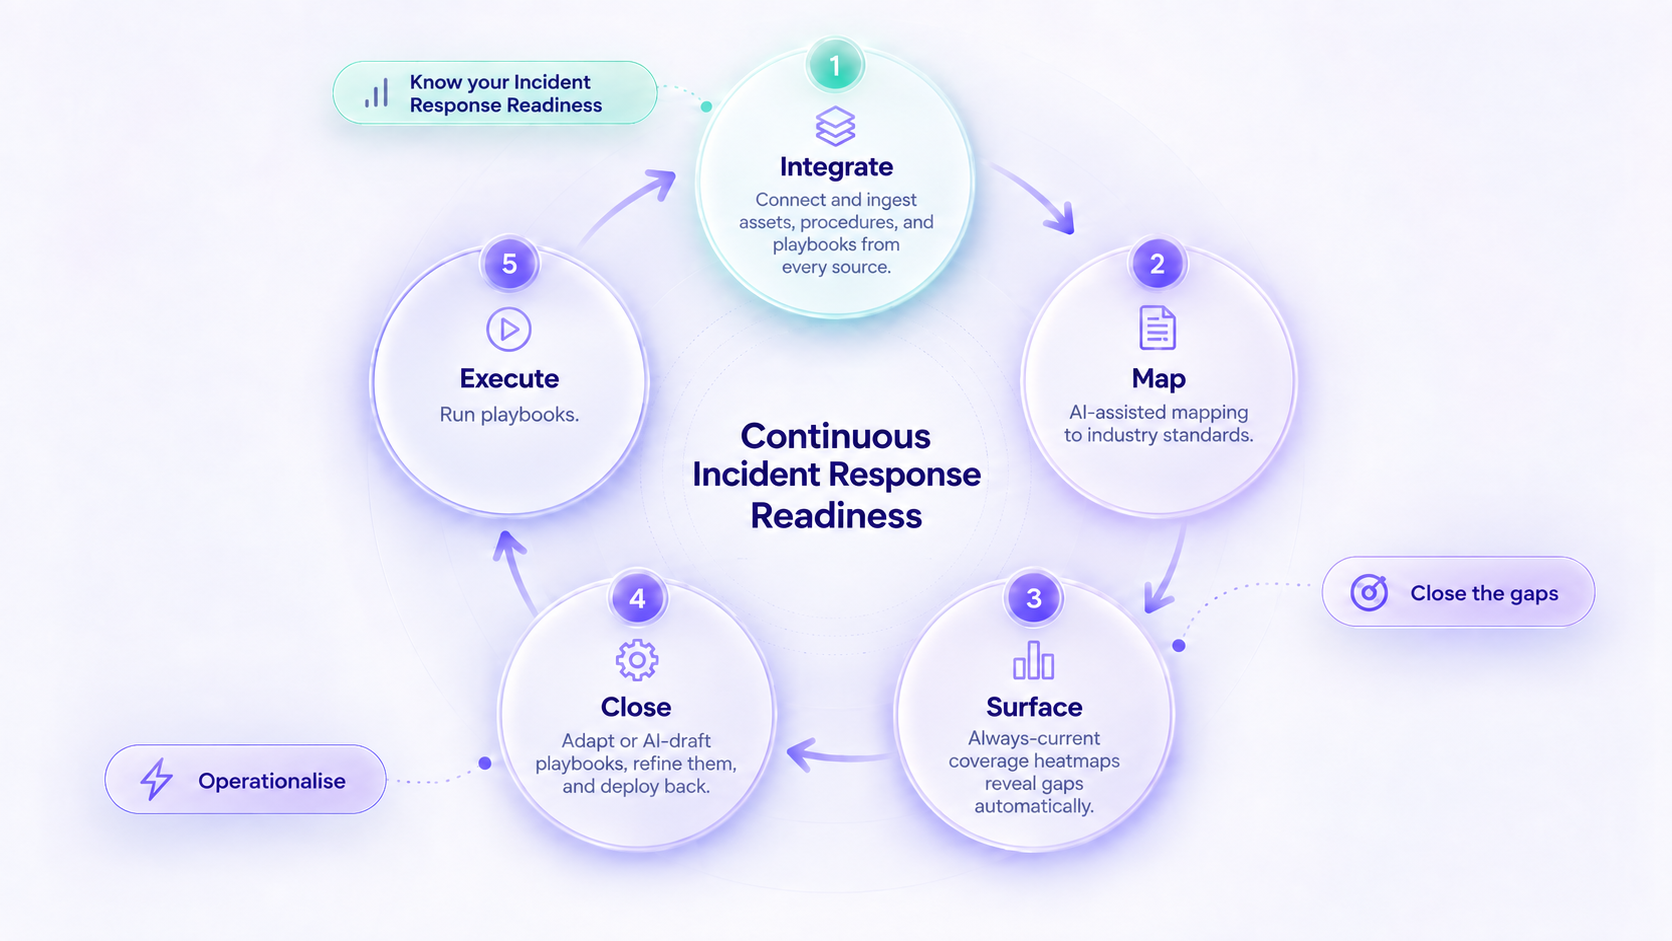
Your response readiness stays current as your environment, procedures, and lessons learned evolve.
Your wins with Cymph
From keeping playbooks current to identifying readiness gaps, Cymph gives your team the visibility and control needed to continuously improve incident response.

Continuously playbook governance: keep ownership, reviews, and testing schedules current

Risk closed before it materialises: gap analysis over always up-to-date framework content

Assurance that survives changes: keep everything up-to-date against any pace of infrastructure and team changes

A team that gets stronger every cycle: test and execute with confidence against up-to-date procedures
How Cymph helps each role
Whether you're a CISO, SOC Manager, Incident Responder, or part of a cross-functional team, Cymph helps you improve incident response readiness, execution, and collaboration.

CISO
Answer the board's incident response readiness question with data.
Have audit-ready framework alignment reports on demand.
Demonstrate continuous improvement, not just point-in-time snapshots.

SOC Manager
See which threats lack procedures and playbooks. Stop mapping response coverage manually.
Give analysts a single, always-current source of structured, ready-to-use playbooks.
Adapt quickly and accurately as threats and environments change.

Cross-function
Cybersecurity is no longer a single-team effort.
With Cymph, every team has a shared place to reference during an incident, helping everyone stay aligned and respond consistently.
Test and improve readiness across the enterpise.
Have questions?
Find quick answers below or contact us for other questions.
Can Cymph run on-premises or is it a cloud-only solution?
Cymph can run both on-premises and as a managed cloud tenant.
Who owns the data? Do I need to disrupt my existing workflows?
There is absolutely no requirement to disrupt your existing workflows and process. Cymph operates as a vendor-agnostic layer on top of the tools and products you already use.
How does it work with AI? Who pays it?
The platform comes with the Bring-Your-Own-AI (BYOAI) model. You can configure the AI provider and desired model from the configuration panel.
What happens if an integration is missing?
If you need a new integration, get in touch with our team.